
PROGRAM DESCRIPTION
When a cyberattack hits, the CFO is not a bystander — within hours, they are managing liquidity, disclosure obligations, insurance claims, vendor payments, and board communications, often with incomplete information and a room full of people looking to finance for answers. Most cybersecurity training is built for IT and security teams; very little prepares the finance function for the operational, financial, and reputational decisions a crisis forces in real time.
Cyber Crisis Command: Finance Leadership in the War Room is a scenario-driven program built in consultation with the Department of Homeland Security’s cybersecurity guidance and incident response frameworks. It places CFOs and senior finance leaders directly into simulated breach scenarios — ransomware, business email compromise, third-party/vendor breaches, and critical systems outages — to practice the decisions finance uniquely owns: activating cyber insurance, managing ransom payment decisions, securing emergency liquidity, maintaining payroll and vendor continuity, and meeting SEC and regulatory disclosure timelines.
Participants will work through a live tabletop exercise modeled on DHS/CISA incident response protocols, alongside sessions on the finance-specific fundamentals: what cyber insurance actually covers (and where the gaps are), how to build a cyber-incident financial continuity plan before a crisis hits, and how to communicate with the board, auditors, and regulators when facts are still emerging. The program closes with a practical toolkit finance leaders can bring back and adapt into their own organization’s incident response plan.
Who should attend: CFOs, Treasurers, Controllers, and senior finance leaders responsible for financial continuity, risk management, insurance, or regulatory disclosure during a cybersecurity incident.
KEY TAKEAWAYS
- Know finance’s role in the incident response chain — understand where CFO decisions fit alongside IT, legal, and executive leadership during an active incident, using DHS/CISA incident response frameworks as the shared playbook.
- Run the financial continuity plan — maintain payroll, vendor payments, and emergency liquidity when core systems are compromised or offline.
- Navigate the ransom payment decision — understand the financial, legal, and regulatory considerations (OFAC exposure, insurance requirements, law enforcement coordination) before a ransom demand ever arrives.
- Stress-test cyber insurance coverage — identify common coverage gaps, sub-limits, and exclusions before a claim is needed, not after.
- Meet disclosure obligations under pressure — understand SEC cyber incident disclosure timelines and how to coordinate accurate, defensible communication while facts are still developing.
- Lead board and stakeholder communication — deliver clear, credible updates to the board, auditors, and investors during a live incident, without over- or under-committing to unconfirmed facts.
- Build (and rehearse) a finance-specific incident response plan — leave with a scenario-tested template to adapt internally, plus a rationale for running regular tabletop exercises.
SPEAKERS
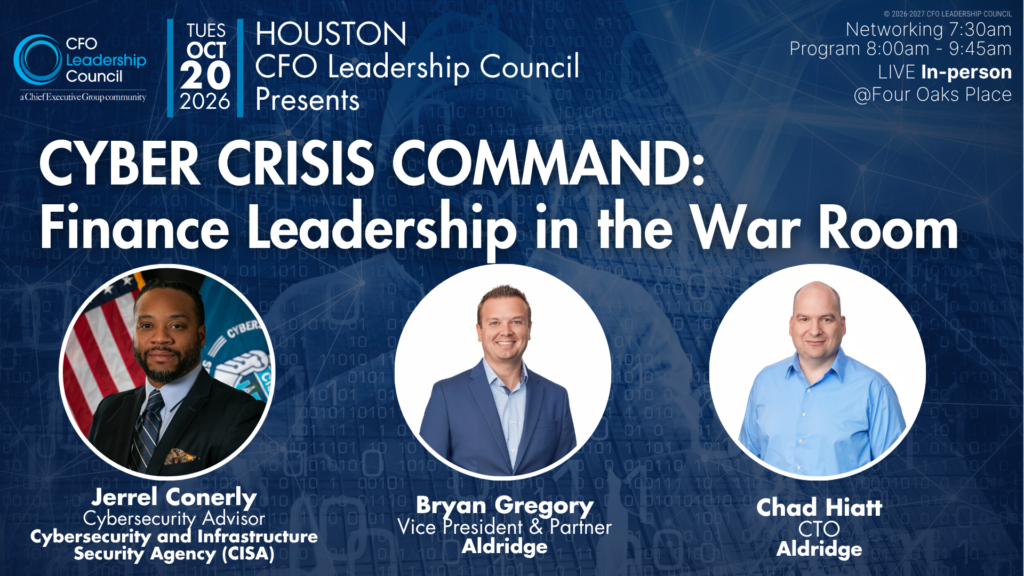
Jerrel Conerly | Cybersecurity Advisor | Cybersecurity and Infrastructure Security Agency (CISA)
Jerrel Conerly is Cybersecurity Advisor for the Cybersecurity and Infrastructure Security Agency (CISA), Region 6, in Houston, TX. with the charge of helping critical infrastructure owners and operators protect critical infrastructure from cyber threats and enhance resilience through voluntary and non-regulatory collaboration. This includes private sector owners, operators, and employees; state, local, tribal, and territorial (SLTT) officials; and other federal agencies.
Mr. Conerly previously served as an Information System Security Officer with the Department of Veteran Affairs, as the designated Lead in support of the Financial Services Center in Austin, TX. He developed technical solutions, guidance, and specifications for the National Data Center security program. His focus areas included Data Centers, Data Systems/Services, Cooperative Research and Development Agreements, Cloud Security, Storage Area Networks, Virtual Desktop and Infrastructure (VDI), Application Security, Change Management, Risk Management, Continuity of Operations (COOP), Disaster Recovery, Blockchain and Robotic Process Automation.
Bryan Gregory | Vice President & Partner | Aldridge
Bryan Gregory is Vice President & Partner at Aldridge, a Houston-based managed IT and cybersecurity firm serving mid-market companies. Since joining Aldridge in 2008, Bryan has helped organizations solve their most pressing technology challenges, from strengthening cybersecurity defenses to adopting emerging tools like AI responsibly. He works closely with CFOs and finance leaders to reduce risk, control technology costs, and ensure IT investments deliver measurable business value.
Chad Hiatt | CTO | Aldridge
At Aldridge, Chad is the Chief Technology Officer (CTO). His role entails working to further advance the company’s technology strengths, thought leadership, and value delivery to clients. Chad’s technology career began early, programming his own games as a kid and writing educational software in grade school. Chad started his first IT company before he could drive, and during the 30 years of his career, has developed into a technology and security architect with the skills to identify, align, and execute the IT strategies and initiatives of organizations across a variety of industries.
EVENT POLICIES AND RESOURCES
Please visit our Events Policies and Resources page for information about chapter leadership, support, CPE, attendance, cancelations and more.
SPONSOR PARTNERS
Thank you to our valued Sponsor Partners. This event is open to members, sponsors, and special guests.